 Bahrain, Saudi Arabia


 Bahrain
 Saudi Arabia
Securing Regulation and Compliance Driven Organizations
Cyberattacks Targeting Regulation and Compliance
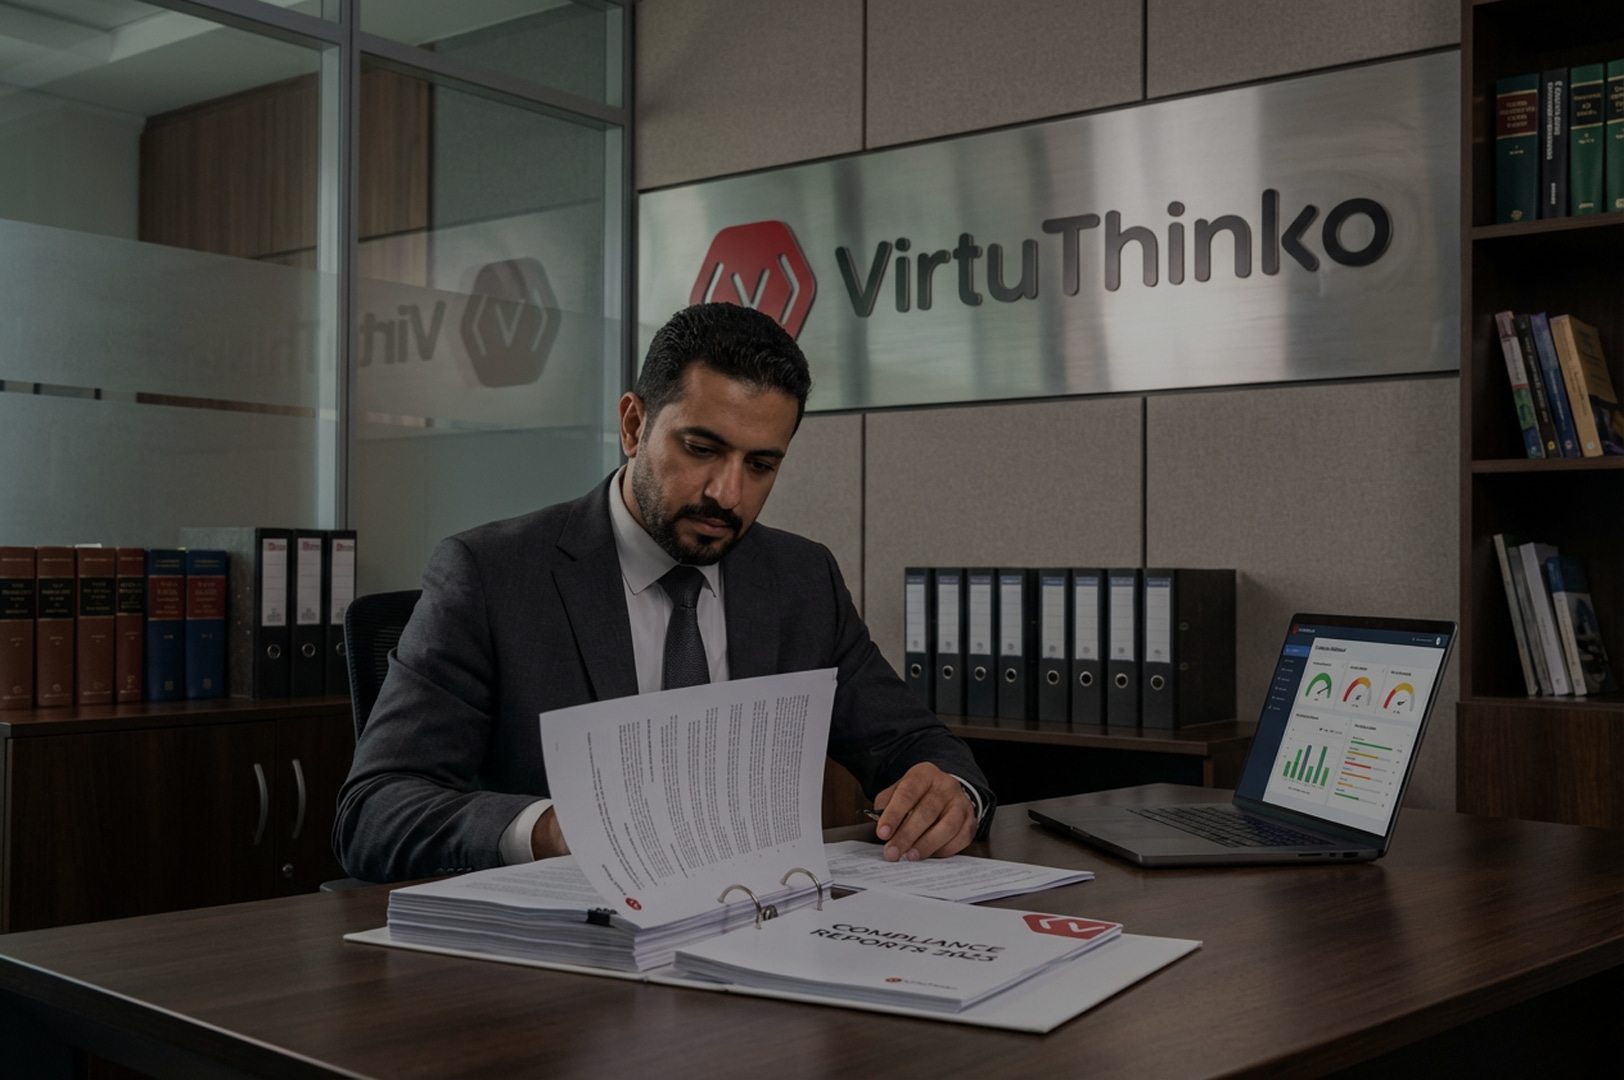
Regulatory bodies, supervisory authorities, law firms, and compliance driven organizations handle highly sensitive information such as case files, investigations, audits, financial records, and citizen or client data. This makes them attractive targets for cybercriminals who seek to steal confidential documents, influence decisions, or disrupt regulatory processes. Breaches in this space can lead to legal consequences, loss of public trust, exposure of privileged information, and significant regulatory fines. As regulations such as GDPR, CCPA and sector specific frameworks become stricter, organizations must prove that their systems, processes, and data handling practices are secure, transparent, and auditable.
State of Regulation and Compliance
$4.88 Million
Average global cost of a data breach (IBM, 2024)
48%
Of organizations fined after a breach, share whose fine exceeded USD 100,000 (IBM, 2025)
12,195
Confirmed data breaches analysed worldwide in Verizon's 2025 DBIR (22,052 incidents)
How VirtuThinko Helps Regulation and Compliance

Governance, Risk and Compliance Enablement
VirtuThinko provides integrated Governance, Risk and Compliance solutions that help organizations map regulations to controls, visualize risk across the environment, and measure compliance posture. This supports regulators, legal teams, and compliance officers with clear dashboards, risk quantification, and evidence that policies and technical controls are in place and working effectively.

Testing, Assurance and Regulatory Readiness
Through cybersecurity testing and assurance services, VirtuThinko performs risk assessments, vulnerability assessments, configuration reviews, and security testing that align with regulatory and framework requirements. This helps organizations prepare for external audits, demonstrate control effectiveness, and close gaps before they become reportable incidents.

Secure Data Handling and Evidence Management
Regulators, law firms, and compliance teams must manage large volumes of confidential documents and evidence. VirtuThinko’s data protection and device security capabilities support encryption, access control, endpoint hardening, and secure collaboration so that case files, reports, and legal documents remain protected throughout their lifecycle.

Policy, Framework and Continuous Compliance Support
VirtuThinko helps organizations design, implement, and maintain policies that align with relevant regulations and frameworks such as GDPR, PCI DSS, NIST based controls, and local data protection laws. Combined with monitoring and reporting, this supports continuous compliance rather than one time audit preparation, reducing the likelihood of fines and improving transparency for regulators and stakeholders.
Protecting Sensitive Data in Regulation and Compliance
Regulatory and compliance driven organizations have a responsibility to protect confidential information while ensuring that laws and standards are enforced fairly and consistently. By combining strong governance, continuous assurance, secure data handling, and clear reporting, these organizations can lower the risk of breaches, reduce regulatory penalties, and maintain trust with citizens, clients, and regulated entities.
VirtuThinko helps organisations design, implement and maintain policies that align with relevant regulations and frameworks such as GDPR, PCI DSS, NIST based controls and local data protection laws. Which obligations apply to a specific organisation depends on its circumstances, so this is general information rather than legal advice and should be confirmed with a qualified professional.
They are targeted because they handle highly sensitive information such as case files, investigations, audits, financial records and citizen or client data. Attackers seek to steal confidential documents, influence decisions or disrupt regulatory processes. Breaches can lead to legal consequences, loss of public trust, exposure of privileged information and significant regulatory fines.
Through cybersecurity testing and assurance services, VirtuThinko performs risk assessments, vulnerability assessments, configuration reviews and security testing that align with regulatory and framework requirements. This helps organisations prepare for external audits, demonstrate control effectiveness and close gaps before they become reportable incidents. Governance, Risk and Compliance solutions add dashboards, risk quantification and evidence that controls are working.
Continuous compliance means maintaining aligned policies supported by ongoing monitoring and reporting, rather than one-time audit preparation. This approach reduces the likelihood of fines and improves transparency for regulators and stakeholders. It reflects a wider expectation that organisations prove their systems, processes and data handling practices are secure, transparent and auditable.